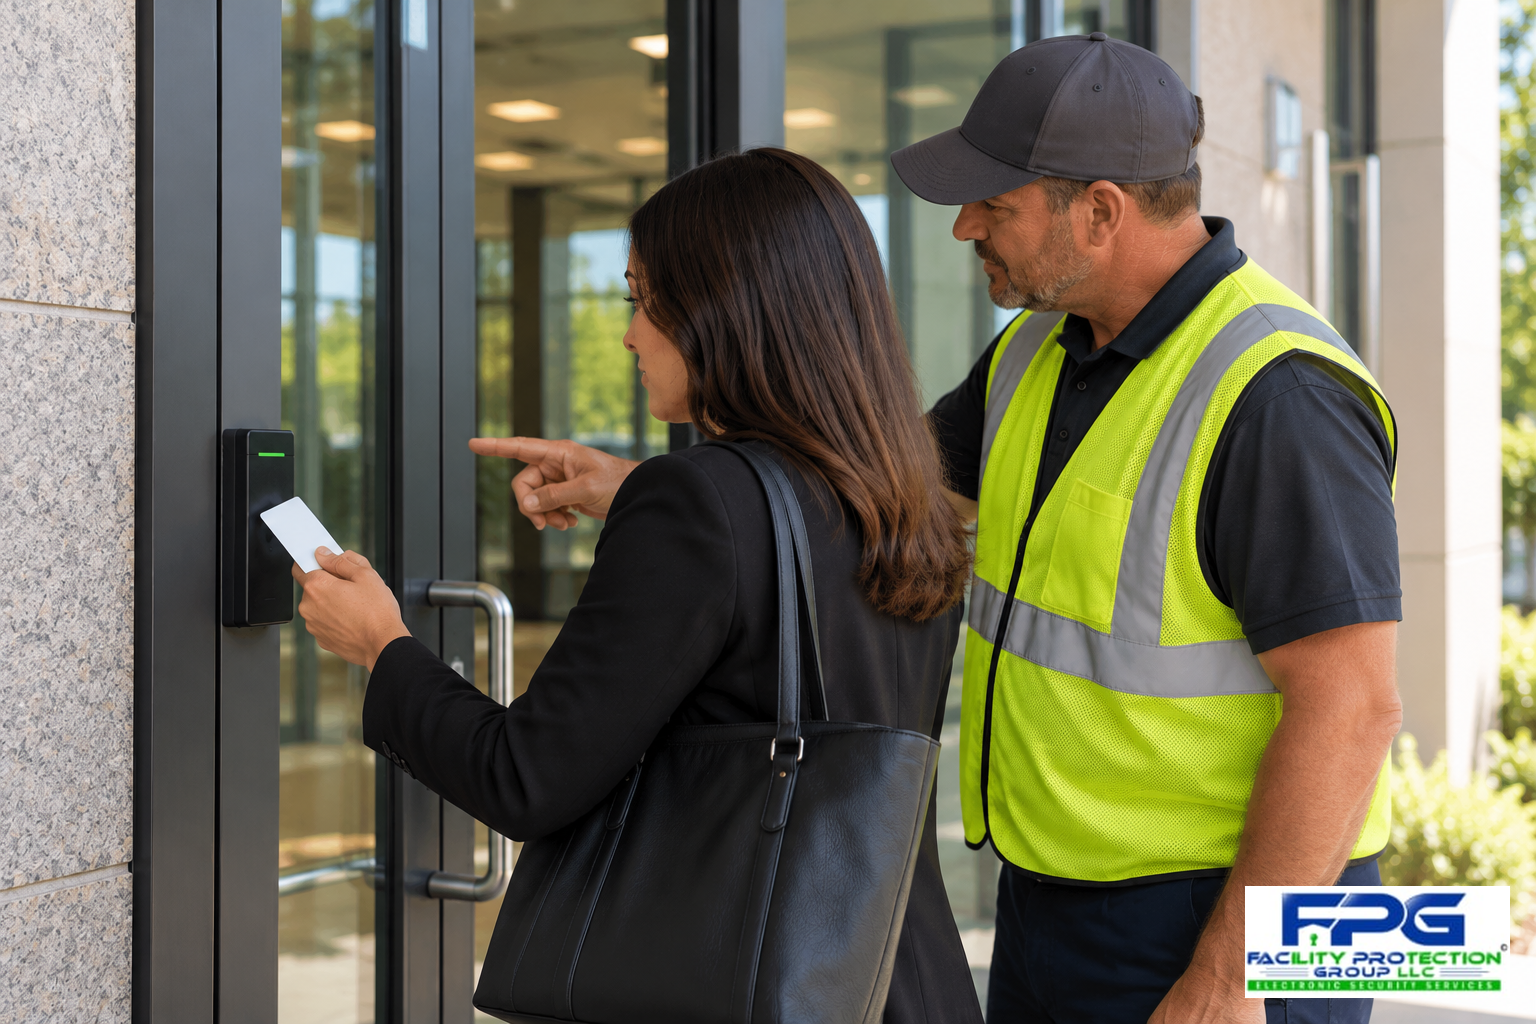
Access control becomes more complicated when a business must manage employees, contractors, vendors, and other authorized visitors who have different reasons for entering the property. Employees may need regular access to offices and work areas, while contractors require temporary entry to specific locations. Vendors may need access to delivery entrances, loading docks, or designated service areas without entering the rest of the facility. When these differences are not properly managed, businesses can unintentionally create security gaps that expose people, property, equipment, and sensitive information to unnecessary risk.
Many commercial facilities begin with a relatively simple approach to building entry. Employees receive keys, access cards, or door codes, and outside personnel are admitted when needed. As the business grows, however, the number of authorized users increases, responsibilities change, and additional doors may need to be secured. A system that once seemed adequate can become difficult to manage, particularly when administrators cannot easily determine who should have access, which areas they may enter, or when their permissions should expire.
The challenge is not simply keeping unauthorized individuals outside the building. It is making sure authorized people can reach the areas necessary for their responsibilities without gaining access to locations where they do not belong. A well-planned commercial access control system can help businesses establish those boundaries, simplify credential management, and respond more efficiently when staffing or operational requirements change.
For business owners, facility managers, property managers, and security directors, the objective should be a practical entry-management strategy that supports daily operations while reducing avoidable security risks. Understanding where access problems originate is the first step toward developing a solution that fits the facility.
Table of Contents
- Why Is Managing Employee, Contractor and Vendor Access So Difficult?
- How Can Access Control Assign the Right Permissions to Each Person?
- How Should Businesses Manage Temporary Contractor and Vendor Access?
- How Can Businesses Reduce Risks from Shared Keys, Cards and Door Codes?
- How Can Access Records Improve Accountability and Security?
- What Common Access Management Mistakes Should Businesses Avoid?
- When Should a Business Reevaluate Its Access Control System?
Why Is Managing Employee, Contractor and Vendor Access So Difficult?
Commercial buildings rarely operate with a single category of authorized user. A typical business may have full-time employees, part-time personnel, managers, maintenance technicians, cleaning contractors, delivery services, equipment vendors, and outside professionals who require access for specific assignments. Although these individuals may all have legitimate reasons to enter the property, their access requirements are seldom identical.
An employee working in an administrative office may need access during normal business hours but have no reason to enter a server room, inventory storage area, or mechanical equipment space. A maintenance contractor may require entry to those restricted locations but only while completing an approved service assignment. A cleaning company may need access after normal operating hours, while delivery personnel may require entry to a receiving area without being permitted into employee workspaces.
Problems develop when a business treats these different access requirements as though they were interchangeable. Issuing unrestricted credentials for convenience can provide individuals with more access than their responsibilities require. Sharing door codes among multiple contractors may make entry easier initially, but it becomes difficult to determine who still knows the code after assignments end. Physical keys present a similar challenge because businesses may not know whether copies have been made or returned.
Personnel changes create additional complications. Employees are hired, promoted, transferred, or separated from the company. Contractors complete projects, vendors change service representatives, and temporary workers may return for future assignments. If access permissions are not updated as these changes occur, credentials can remain active long after they are needed.
These problems become more pronounced in facilities with multiple departments, entrances, shifts, or restricted areas. A warehouse may have separate office, inventory, loading dock, and equipment rooms. A manufacturing facility may need to distinguish production personnel from administrative employees and outside maintenance providers. A healthcare or professional services facility may have additional reasons to limit access to records, specialized equipment, and sensitive work areas.
The underlying issue is often a lack of consistent access management rather than a shortage of security equipment. Businesses need a clear understanding of who requires entry, where they are permitted to go, and when those permissions should be available. Without those rules, even an electronic access control system can become difficult to administer effectively.
A more organized approach begins by identifying the facility’s entry points, dividing users into appropriate categories, and establishing access permissions that reflect actual responsibilities. These decisions provide the foundation for a system that is easier to manage and better aligned with the organization’s daily operations.
How Can Access Control Assign the Right Permissions to Each Person?
One of the most useful capabilities of a properly configured commercial access control system is the ability to establish different permissions for different groups of users. Instead of issuing identical credentials to everyone, administrators can determine which doors an individual may use and, when supported by the system, the days and times those permissions are valid.
For example, an office employee might be authorized to enter the main building entrance and assigned department during scheduled working hours. A supervisor may have broader access to certain operational areas, while a maintenance technician may require entry to mechanical rooms or equipment spaces. A delivery vendor could be restricted to a receiving entrance, and a cleaning contractor could be permitted to enter designated areas during an approved evening schedule.
This approach is commonly referred to as role-based access management. Rather than making every permission decision individually, administrators can establish access groups based on job responsibilities or operational needs. When a new employee joins the organization, the appropriate permissions can be assigned according to the person’s role. When responsibilities change, those permissions can be adjusted without replacing the entire system.
Access groups also help reduce administrative errors. A business that manages dozens or hundreds of credentials can struggle when every user has a different combination of permissions. Establishing consistent groups creates a more understandable structure and makes it easier to review whether people still have the access they require.
However, access groups should not be created solely for convenience. A single group that opens nearly every door may simplify initial programming but undermine the purpose of controlling access. A better strategy is to follow the principle of least privilege: provide the access necessary to perform an authorized responsibility without granting unnecessary entry to unrelated areas.
Time schedules add another level of control. A contractor authorized to work in a mechanical room between 8:00 a.m. and 5:00 p.m. may not need the ability to enter the building late at night. Similarly, an employee assigned to a weekday office schedule may not require unrestricted weekend access. When properly configured, time-based permissions can help align entry privileges with legitimate operational requirements.
Effective access management also requires an administrative process for approving and changing permissions. Facility managers should know who is authorized to request access, who can approve restricted-area entry, and who is responsible for updating the system. Without clear administrative responsibility, permission groups can gradually become inconsistent as employees and contractors change roles.
Importantly, access control does not eliminate the need for sound physical security practices. A credential may authorize entry through a controlled door, but it does not necessarily prevent someone else from following an authorized person into the building. Door hardware, visitor procedures, employee awareness, and appropriate monitoring remain important parts of a broader security strategy.
For businesses evaluating an existing system, the central question is whether administrators can easily answer three questions: Who currently has access? Which areas can they enter? When are they permitted to enter? If those answers are unclear or difficult to obtain, the organization may benefit from reviewing its credential structure, access groups, and administrative procedures.
How Should Businesses Manage Temporary Contractor and Vendor Access?
Contractors and vendors are essential to the operation of many commercial facilities, but their access requirements are often different from those of permanent employees. A maintenance company may need to service equipment for several days, an IT contractor may require occasional entry to a restricted communications room, and a delivery vendor may visit the same receiving area several times each week. Providing these individuals with unrestricted building access can create unnecessary exposure, particularly when their assignments involve areas containing valuable equipment, inventory, or sensitive business information.
A practical access control strategy begins by determining exactly what outside personnel need to accomplish. Before issuing a credential, the business should identify the authorized work area, the expected duration of the assignment, the appropriate entrance, and whether access is needed during normal operating hours or at another scheduled time. These decisions help prevent temporary access from becoming a permanent security exception.
For example, consider a contractor hired to replace equipment in a building’s mechanical room. The contractor may need access through a designated service entrance and permission to enter the mechanical room for three business days. There is generally no operational reason to provide access to executive offices, inventory storage, or unrelated departments. By assigning permissions that match the approved work, the business can support the project without unnecessarily expanding the contractor’s access.
Electronic credentials can make this process more manageable. Depending on the capabilities of the installed system, administrators may be able to establish activation dates, expiration dates, time schedules, and door-specific permissions. A temporary credential can be configured for the expected assignment rather than relying on a physical key or shared code that may remain usable after the work is complete.
However, expiration settings should not replace active oversight. Projects may finish early, contractors may change personnel, and service agreements may be terminated unexpectedly. Businesses should establish a procedure for promptly disabling credentials when authorization ends, even when an automatic expiration date has already been assigned.
Vendor access presents a related challenge because some service providers return regularly. A cleaning company, landscaping contractor, equipment maintenance provider, or delivery service may require recurring access, but not necessarily the same permissions as an employee. Creating appropriate vendor access groups can simplify recurring visits while maintaining boundaries around restricted areas.
In some facilities, additional verification may be appropriate before a contractor enters sensitive locations. A supervisor may need to approve access, a visitor may require an escort, or a work order may need to be confirmed. Electronic access control can support these procedures, but the organization’s operating policies determine when additional authorization is necessary.
Businesses should also distinguish between identifying an individual and authorizing entry. A credential assigned to a contracting company does not automatically establish which employee of that company is using it. Where accountability is important, credentials should be assigned to identifiable individuals rather than passed among workers. This helps administrators manage permissions more accurately and makes access records more useful when questions arise.
The objective is not to make contractor or vendor entry unnecessarily difficult. It is to create a repeatable process that allows approved work to proceed while maintaining reasonable control over where outside personnel can go and how long their permissions remain active.
How Can Businesses Reduce Risks from Shared Keys, Cards and Door Codes?
Many access management problems begin with credentials that are difficult to track or revoke. Traditional metal keys, shared keypad codes, and electronic access cards can all provide legitimate entry, but each method has different administrative and security considerations. The most appropriate approach depends on the facility, the number of users, the sensitivity of protected areas, and the capabilities of the installed system.
Physical keys remain useful in many applications, particularly where electronic access is unnecessary or impractical. However, keys can become difficult to manage when employees change positions, contractors complete assignments, or multiple copies circulate among departments. If a key is lost or not returned, a business may need to rekey affected locks to restore confidence that access is properly controlled.
Shared keypad codes create another challenge. A single code may initially seem convenient for employees, service technicians, or cleaning personnel, but the organization loses control as more people learn it. When someone leaves the company or a contractor’s assignment ends, administrators may have no reliable way to determine whether the code has been shared with others. Changing the code may also require notifying every remaining authorized user.
Individual electronic credentials offer a more manageable alternative when supported by an appropriately designed access control system. A card, key fob, or mobile credential can be associated with a specific user account and assigned permissions based on that person’s responsibilities. If the credential is lost or the individual is no longer authorized, an administrator can generally disable that credential without changing every other user’s access.
Not all electronic credentials provide the same level of protection. Some older proximity technologies rely on identifiers that may be vulnerable to duplication, while modern encrypted credential technologies can provide stronger protection when the readers, credentials, and system configuration support the appropriate security features. Businesses evaluating a system should consider credential security as well as convenience, particularly when protecting sensitive or high-value areas.
Mobile credentials may offer additional administrative flexibility in compatible systems. Depending on the platform, an administrator may be able to issue or revoke a credential without physically distributing a card. However, mobile access should be evaluated in relation to device compatibility, user enrollment, network requirements, security policies, and the organization’s ability to support employees who cannot or do not wish to use personal devices for workplace entry.
Credential management also requires clear procedures. A business should establish how credentials are requested, approved, issued, replaced, suspended, and permanently deactivated. These responsibilities should not depend entirely on one employee’s informal knowledge of the system. Documented procedures help maintain consistency when administrators change or when the organization grows.
Periodic credential reviews are particularly important. An access database may contain former employees, inactive contractors, duplicate accounts, and permissions that no longer reflect current responsibilities. Reviewing active users and their assigned access groups can help identify unnecessary privileges before they become a larger operational concern.
For facilities considering modernization, replacing outdated credential practices may provide meaningful benefits even when the existing doors and other portions of the security infrastructure remain serviceable. The appropriate upgrade path should be determined through a review of system compatibility, existing hardware, operational needs, and the security level required for each protected area.
How Can Access Records Improve Accountability and Security?
Controlling who may enter a building is only one part of effective access management. Businesses may also need to understand when credentials were used, which doors were involved, and whether unusual activity requires further investigation. Commercial access control systems with event-recording capabilities can provide information that supports these operational and security responsibilities.
When a properly configured system records a credential transaction, the event may include the credential or user associated with the activity, the controlled door, the date and time, and whether access was granted or denied. The specific information available depends on the equipment, software, system settings, and applicable retention policies.
These records can help facility managers answer practical questions. If a restricted storage room was accessed outside normal operating hours, administrators may be able to review the associated access events. If a contractor reports being unable to enter an approved work area, the system’s event history may help determine whether the credential was presented, whether permission was denied, or whether another issue requires attention.
Access records may also help identify patterns that deserve review. Repeated denied-entry attempts at a restricted door, credential activity outside an expected schedule, or continued use of an account assigned to a former contractor can indicate a need to verify permissions or investigate the circumstances. Such activity does not automatically establish wrongdoing, but it can provide useful information for an appropriate response.
There is an important limitation: a credential transaction does not necessarily prove which individual physically passed through a doorway. A card may be shared, another person may follow an authorized user, or a door may be held open. For that reason, access event records should be understood as evidence of system activity rather than a complete record of every person’s movement.
Where greater situational awareness is required, businesses may benefit from integrating access control with video surveillance or other security technologies. When compatible systems are properly configured, a door event may be associated with relevant camera footage, helping authorized personnel review the circumstances surrounding an entry attempt. This can be particularly useful at receiving entrances, restricted equipment rooms, and other locations where verification matters.
Facility managers should also consider how access information is protected. User records, credential identifiers, event histories, and administrative accounts may contain sensitive operational or personal information. Access to these records should be limited to authorized personnel, and system administration should follow appropriate cybersecurity and privacy practices.
The National Institute of Standards and Technology provides a useful framework for managing cybersecurity risks through its Cybersecurity Framework. Although the framework is not specific to commercial door access control, its emphasis on identifying risks, protecting systems, detecting events, responding to incidents, and recovering operations offers a relevant foundation for evaluating connected security technologies.
Record retention is another consideration. Keeping event histories indefinitely is not automatically necessary or appropriate. Businesses should establish retention practices based on operational requirements, contractual obligations, applicable laws, and the capabilities of their systems. Administrators should also understand whether records are stored locally, on a network server, or through a cloud-based service, and how those records can be retrieved when needed.
Ultimately, access records are most valuable when they support a defined business purpose. A facility that regularly reviews unusual events, maintains accurate user accounts, and investigates discrepancies is generally better positioned to use the information effectively than one that simply collects records without an established review process.
Facility Protection Group helps commercial organizations evaluate how access permissions, credential management, and system monitoring fit their operational and security requirements. Businesses experiencing difficulties with employee, contractor, or vendor access can benefit from reviewing their existing procedures alongside the capabilities of their installed equipment. A coordinated assessment can help identify practical improvements without assuming that every facility requires the same solution.
What Common Access Management Mistakes Should Businesses Avoid?
Even a professionally installed access control system can become less effective when the policies governing its use are inconsistent or outdated. Businesses sometimes invest in electronic readers, credentials, and management software without establishing clear procedures for issuing access, reviewing permissions, or responding when personnel responsibilities change. Over time, these administrative weaknesses can create security concerns that the original installation was intended to address.
One common mistake is granting more access than an individual actually needs. A new employee may receive the same permissions as a supervisor simply because those settings are convenient to duplicate. A contractor may be assigned an unrestricted credential to avoid the administrative work of identifying the doors required for a particular project. Although these decisions can simplify initial enrollment, they may also allow individuals to enter areas unrelated to their responsibilities.
A better approach is to establish permissions according to actual job functions and approved operational requirements. Administrative personnel, maintenance workers, contractors, vendors, and department supervisors may each need different access groups. These groups should be reviewed periodically to confirm that their permissions remain appropriate as the facility and its operations change.
Another frequent problem involves credentials that remain active after an employee leaves or a contractor completes an assignment. When access management depends on informal communication between departments, the person responsible for disabling credentials may not receive timely notice of a departure. This can leave unnecessary permissions in place, particularly when temporary personnel have worked at the facility for an extended period.
Businesses can reduce this risk by coordinating access control administration with employee onboarding, personnel transfers, contractor approvals, and termination procedures. Human resources, facility management, security personnel, and department supervisors should understand their respective responsibilities. When a person’s authorization changes, the appropriate administrator should receive the information needed to update or revoke access promptly.
Shared credentials present a related concern. A door code used by several contractors or an access card passed between employees may allow authorized work to continue, but it reduces accountability. If an incident occurs, an access record associated with a shared credential may not establish who actually presented it. Individual credentials, combined with clear rules against unauthorized sharing, can help improve the reliability of access management records.
Businesses should also avoid assuming that electronic access control eliminates every vulnerability at a secured entrance. A properly authorized employee may unintentionally allow an unauthorized individual to follow through a door. A door may be propped open for deliveries, or damaged hardware may prevent it from closing and latching correctly. These conditions can undermine an otherwise well-configured system.
Reducing these risks requires attention to the physical doorway as well as the electronic equipment. Door closers, locking hardware, position monitoring, appropriate entry procedures, and employee awareness may all contribute to a more effective installation. The correct combination depends on the location, the building’s operational needs, and applicable life-safety requirements.
Another mistake is overlooking system maintenance. Readers can become damaged, door contacts may stop reporting accurately, and changes to a building’s network or electrical infrastructure can affect connected security equipment. If administrators do not routinely check system operation, a problem may remain unnoticed until someone is unable to enter an authorized area or an incident requires information that was never properly recorded.
Regular testing and maintenance should include the physical condition of controlled doors, credential operation, appropriate event reporting, and the ability of authorized administrators to manage the system. Facilities with multiple entrances or buildings may also need procedures for identifying communication failures and confirming that equipment continues operating as intended.
Cybersecurity deserves similar attention, particularly when access control equipment communicates across a business network or uses remote management services. Unsupported software, shared administrator accounts, weak passwords, and unnecessary network exposure can introduce risks unrelated to the physical doorway. Organizations should coordinate with their IT personnel and security providers to establish appropriate system updates, account permissions, network protections, and recovery procedures.
Finally, businesses should avoid treating access control as a one-time purchase rather than an ongoing operational responsibility. The installation establishes the technical foundation, but continued effectiveness depends on accurate permissions, consistent procedures, working equipment, and periodic review. A system that is properly managed can remain useful as the organization grows, while one that receives little attention may gradually become misaligned with the facility’s security requirements.
When Should a Business Reevaluate Its Access Control System?
Businesses do not necessarily need to replace an access control system simply because it has been in service for several years. However, changes in personnel, building operations, security expectations, and technology can create reasons to reassess whether the existing system continues to meet the organization’s needs. A structured evaluation can help identify practical improvements before administrative problems or equipment limitations become more disruptive.
One important reason for reassessment is organizational growth. A business that originally managed a small number of employees and doors may eventually need to administer hundreds of users across multiple departments, shifts, or buildings. When access permissions become difficult to organize, administrators may begin relying on broad access groups, shared credentials, or manual workarounds that reduce the value of the system.
Changes in contractor and vendor activity can also justify a review. A facility that once admitted occasional service providers may now depend on outside maintenance companies, cleaning personnel, delivery services, technology contractors, and specialized equipment vendors. Each category can introduce different access schedules, restricted areas, and approval requirements. The existing system should be evaluated to determine whether it can support these differences without creating unnecessary administrative complexity.
Personnel turnover is another useful indicator. If former employees remain in the access database, temporary credentials are difficult to deactivate, or administrators cannot readily identify who has permission to enter restricted areas, the organization may need to improve its management procedures. In some cases, the existing equipment can support those improvements through better programming and administration. In others, software or hardware limitations may require a more substantial upgrade.
Facilities should also reevaluate access control when their physical layout changes. New offices, expanded production areas, additional storage rooms, relocated departments, and modified entrances can alter the relationship between authorized users and protected spaces. Permissions that were appropriate for the original building configuration may no longer reflect the way the facility operates.
Security incidents and recurring operational problems provide additional reasons for assessment. Repeated unauthorized entry attempts, missing credentials, doors that are routinely held open, or uncertainty about contractor access can reveal weaknesses that deserve attention. An evaluation should examine the underlying cause rather than automatically assuming that additional equipment is the only solution.
For example, a recurring problem at a receiving entrance might involve a poorly defined delivery procedure, inadequate door hardware, inappropriate access schedules, or insufficient visibility into activity at the entrance. Addressing the issue effectively may require changes to operating procedures, electronic permissions, physical security equipment, or a combination of those measures.
Businesses considering modernization should also examine how their access control system works with other security technologies. Integrating compatible access control and video surveillance systems may help authorized personnel investigate door events and better understand activity around sensitive entrances. An integrated approach can be particularly valuable when the facility must manage multiple security systems that otherwise operate independently.
Facility Protection Group’s Integrated Security Systems Guide provides additional information about coordinating security technologies to support facility protection and operational awareness. Businesses evaluating access management can use this broader perspective to consider how entry control relates to surveillance, intrusion detection, and other protective measures.
It is equally important to determine whether the existing access control platform can support future requirements. Businesses may need additional controlled doors, improved credential management, multiple administrative users, remote management capabilities, or more consistent reporting across locations. Reviewing these requirements before expanding the installation can help avoid incompatible equipment purchases and unnecessary system complexity.
A professional assessment should begin with the facility’s actual operating conditions. This includes identifying the people who require access, reviewing controlled entrances, examining current permission groups, evaluating the condition of door hardware and electronic equipment, and understanding how credentials are issued and revoked. The assessment should also consider applicable building and life-safety requirements, particularly where controlled doors form part of an emergency exit route.
From there, the business can prioritize improvements according to risk, operational importance, and available resources. Some facilities may benefit most from revising access groups and administrative procedures. Others may need to replace outdated readers, improve credential security, expand coverage to additional doors, or modernize an aging management platform. The appropriate recommendation should reflect the specific problems identified during the evaluation.
Businesses seeking a broader understanding of commercial entry security can review Facility Protection Group’s security planning guides, which address access control and related building protection considerations. These resources can help facility managers prepare for discussions about their security requirements and potential system improvements.
The most effective access control strategy is one that remains understandable, manageable, and appropriate for the people who use the building. Employees should be able to enter the areas necessary for their work, contractors and vendors should receive permissions that match their assignments, and administrators should have practical methods for reviewing and changing authorization as circumstances evolve.
Facility Protection Group works with commercial organizations to evaluate security needs and develop solutions that support safer, more manageable building operations. Whether your business is experiencing difficulties with employee access, temporary contractor credentials, vendor entry, or an aging access control installation, a professional review can help identify where improvements may be warranted.
If your organization is struggling to determine who should have access, which doors they should be permitted to use, or how to manage changing personnel requirements, contact Facility Protection Group to discuss your facility’s access control challenges and explore an appropriate approach to improving security and entry management.